📄 仓库 README
在 GitHub 查看 ↗
Unmask the hidden before the world does
An autonomous AI framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then goes further by triaging every finding, implementing code fixes, and opening pull requests on your repository. From first packet to merged patch, with human oversight at every critical step.







LEGAL DISCLAIMER: This tool is intended for authorized security testing, educational purposes, and research only. Never use this system to scan, probe, or attack any system you do not own or have explicit written permission to test. Unauthorized access is illegal and punishable by law. By using this tool, you accept full responsibility for your actions. Read Full Disclaimer
🏆 Flagship result: RedAmon solves 101 / 104 (97.1%) of the XBOW web-security benchmark fully black-box. Every solve ships a complete, unedited raw agent session and a reproducible, step-by-step walkthrough: open any row and read exactly how the flag fell, tool call by tool call. Auditable, line by line. See the XBOW Validation Benchmark scorecard.
📊 Coverage, measured and self-scored: the Bug Bounty Coverage — The Full Taxonomy Audit (PDF, 124 pages) audits RedAmon against all 397 classes of web bug-bounty finding, one line at a time, naming the exact module, skill or scanner behind every verdict, and scoring the recon pipeline and the agentic system separately against their own remit. It is deliberately self-critical, it records what is missing as plainly as what is covered: 134 classes complete, 210 in the build backlog, 44 deliberately excluded, with one explicit decision for every class.
Dynamic Multi-Tool Parallel Recon Pipeline
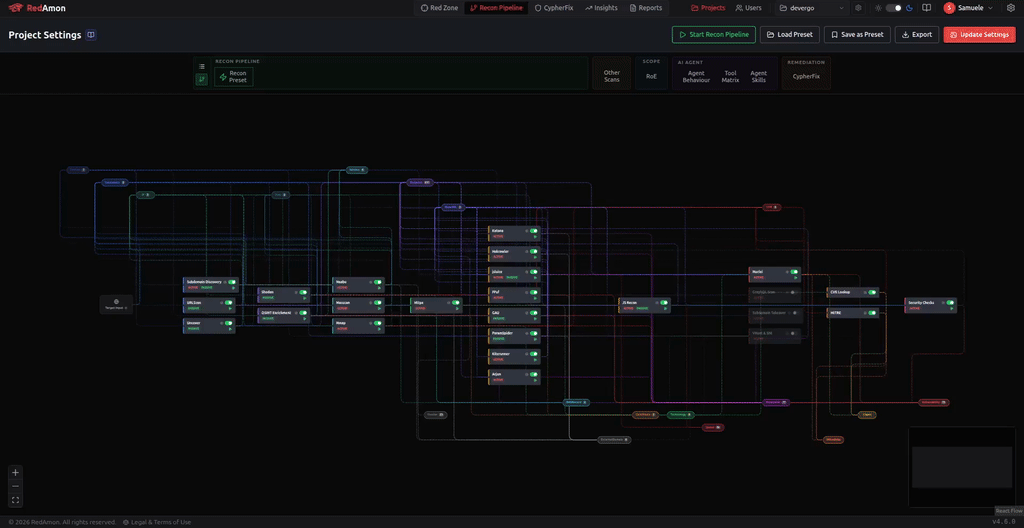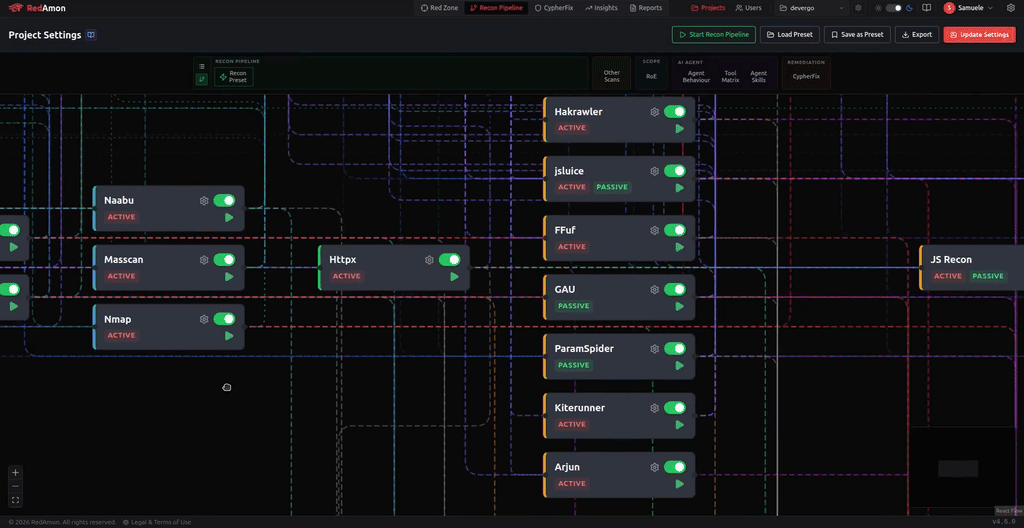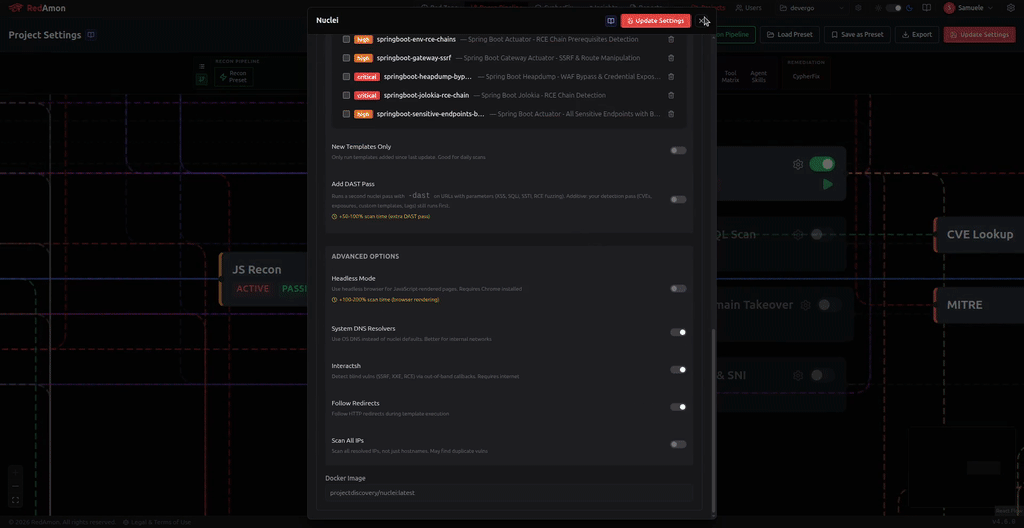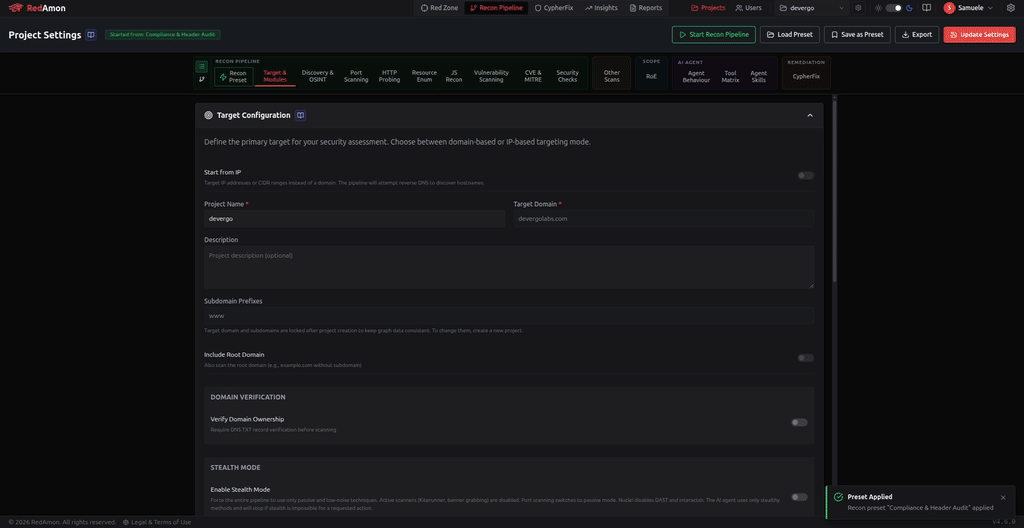
RedAmon launches multiple reconnaissance tools in parallel, each feeding results into a shared knowledge graph in real time. Tools spin up, adapt their scope based on live discoveries, and coordinate without manual intervention. The entire attack surface -- subdomains, ports, endpoints, parameters -- materializes in minutes, not hours.
Recon as a Living Knowledge Graph
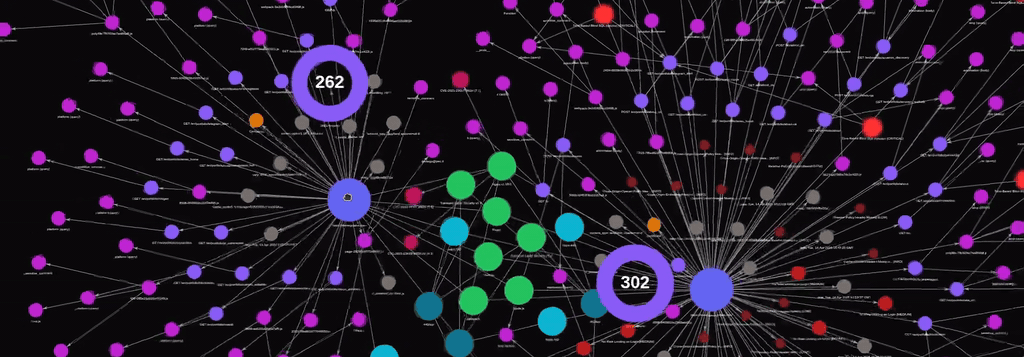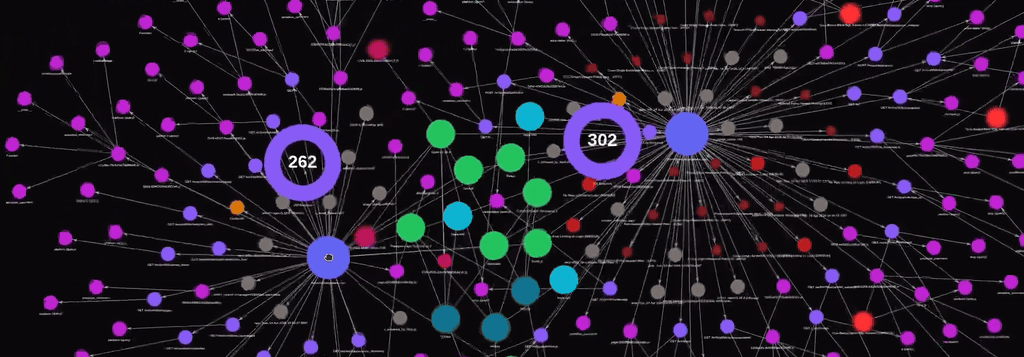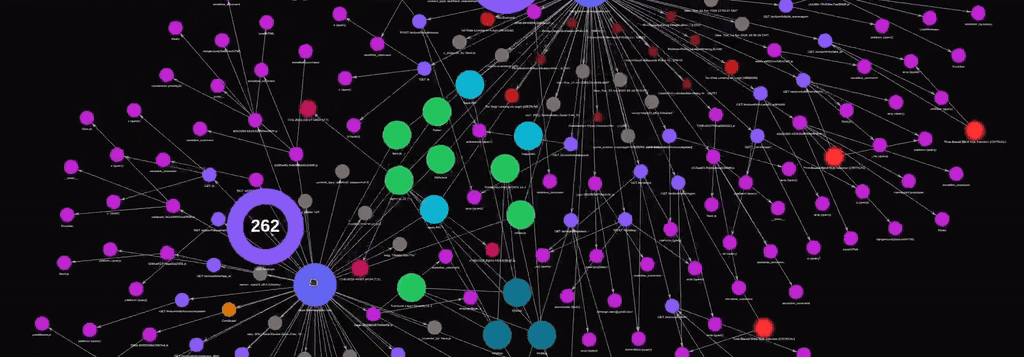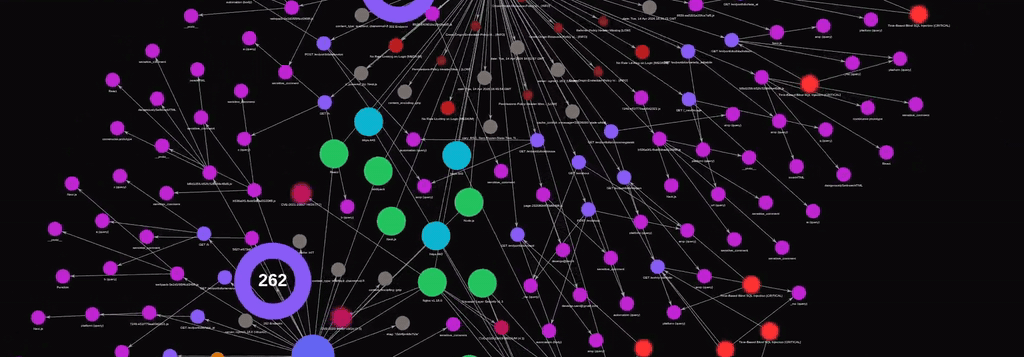
Industry-standard scanners chained so each tool's output feeds the next, then merged into a single Neo4j knowledge graph. Findings are deduplicated, relationships are explicit, and the agent inherits a structured, fully connected attack surface ready to query in natural language.
Offense meets defense. One pipeline, full visibility.
Reconnaissance ➜ Exploitation ➜ Post-Exploitation ➜ AI Triage ➜ CodeFix Agent ➜ GitHub PR
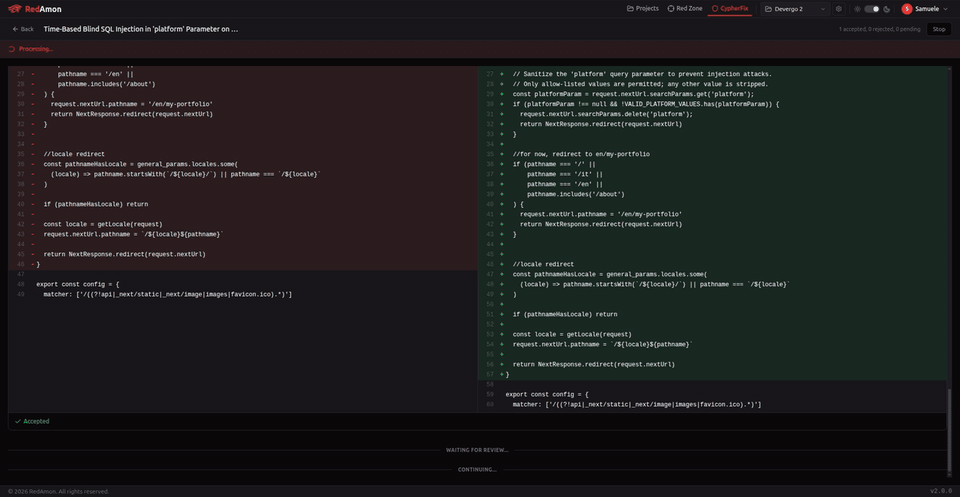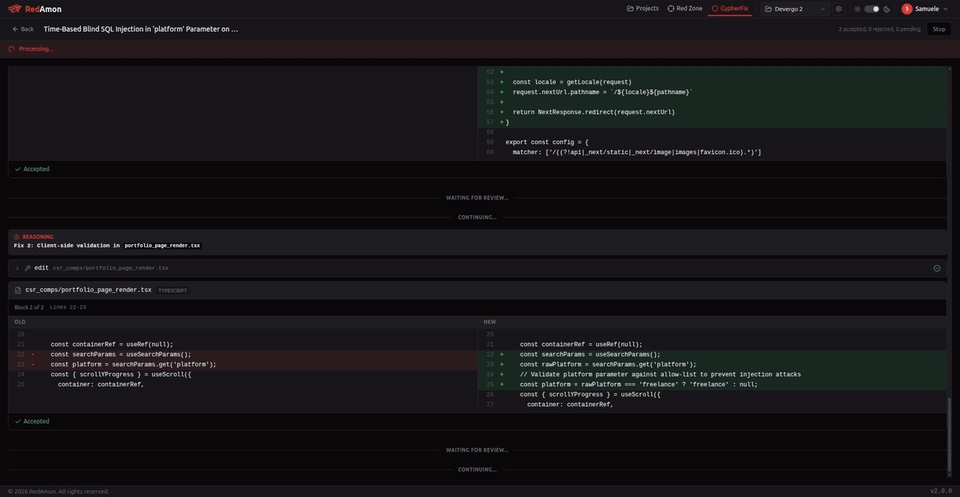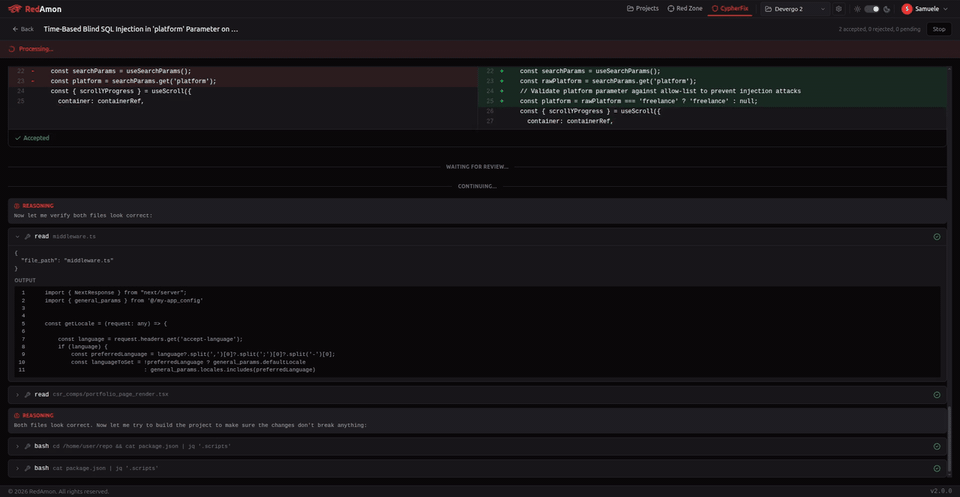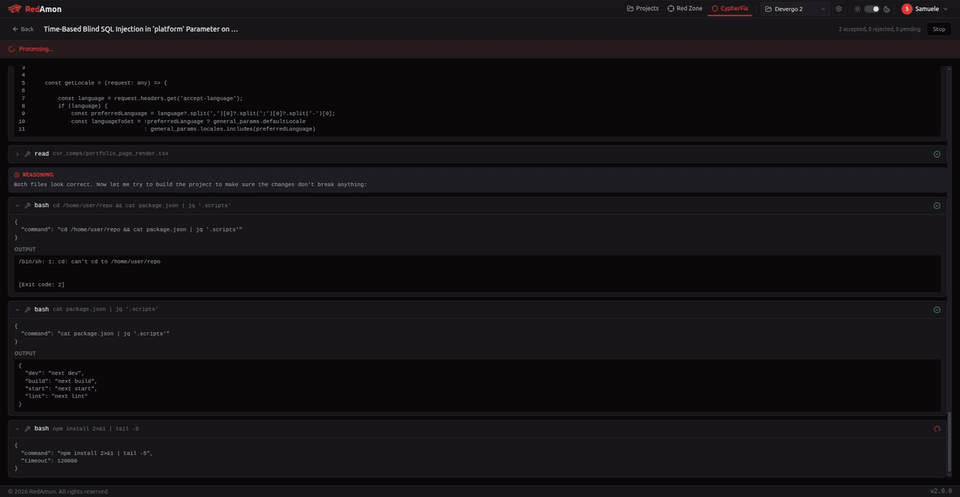
RedAmon doesn't stop at finding vulnerabilities, it fixes them. The pipeline starts with a 6-phase reconnaissance engine that maps your target's entire attack surface, then hands control to an autonomous AI agent that validates CVE exploitability, tests credential policies, and maps lateral movement paths. Every finding is recorded in a Neo4j knowledge graph. When the offensive phase completes, CypherFix takes over: an AI triage agent correlates hundreds of findings, deduplicates them, and ranks them by exploitability. Then a CodeFix agent clones your repository, navigates the codebase with 11 code-aware tools, implements targeted fixes, and opens a GitHub pull request, ready for review and merge.
Roadmap & Community Contributions
We maintain a public Project Board with upcoming features open for community contributions. Pick a task and submit a PR!
Want to contribute? See CONTRIBUTING.md for how to get started.
Maintainers
 Samuele Giampieri: Creator, Maintainer & AI Platform Architect AI Platform Architect & Full-Stack Lead with 15+ years of freelancing experience and more than 30 projects shipped to production, including enterprise-scale AI agentic systems. AWS-certified (DevOps Engineer, ML Specialty) and IBM-certified AI Engineer. Designs end-to-end ML solutions spanning deep learning, NLP, Computer Vision, and AI Agent systems with LangChain/LangGraph. LinkedIn · |
📈 近 7 天 Star 趋势
🏆 排名变化趋势
📋 历史上榜记录
| 日期 | 榜单 | 排名 | 周期新增 | 总 STAR |
|---|