📄 仓库 README
在 GitHub 查看 ↗
Airgorah
A WiFi security auditing software
Installation | Usage | Credits
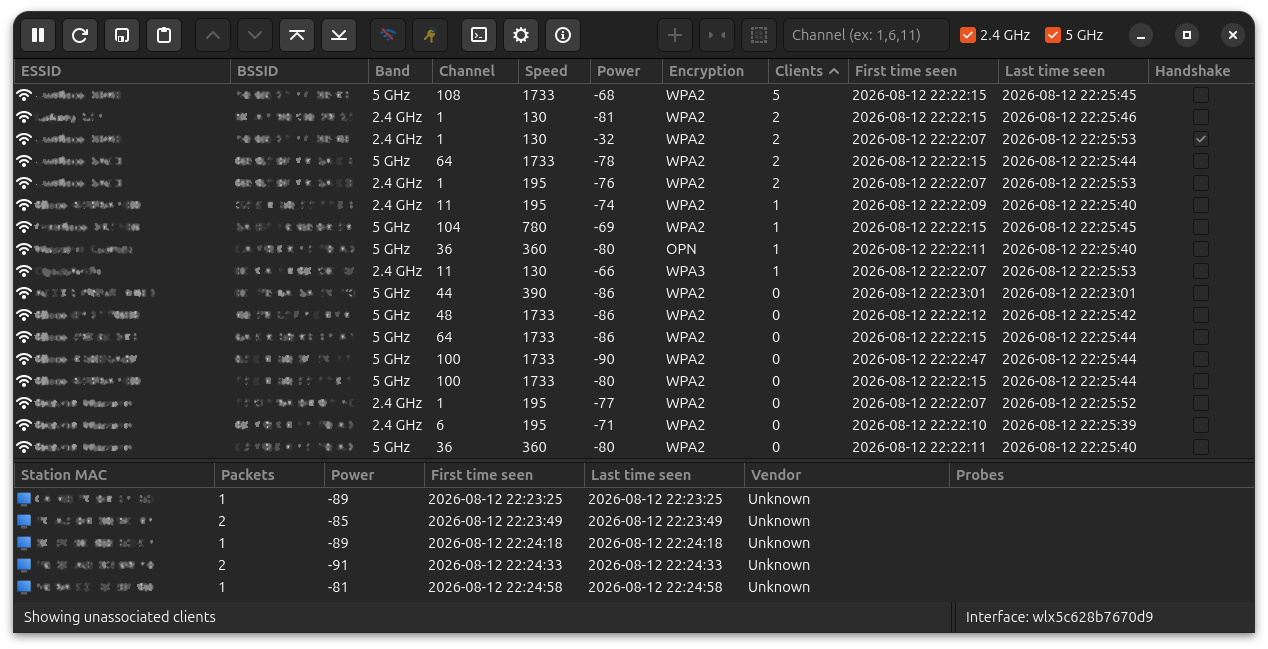


Airgorah is a WiFi security auditing software that can capture nearby WiFi traffic, discover clients connected to access points, perform deauthentication attacks, capture handshakes and PMKIDs, and crack the password of access points.
It is written in Rust and uses GTK4 for the graphical part.
⭐ Don't forget to put a star if you like the project!
Legal
⚠️ Airgorah is designed to be used in testing and discovering flaws in networks you are owner of. Performing attacks on WiFi networks you are not owner of is illegal in almost all countries. I am not responsible for whatever damage you may cause by using this software.
Requirements
This software only works on linux. The graphical interface runs as a normal
user (so it works under both X11 and Wayland). When a privileged operation is
needed, it launches a small privileged agent (airgorah-agent) via polkit,
which will prompt for authentication once.
You will also need a wireless network card that supports monitor mode and packet injection.
Installation
The installation instructions are available here.
Usage
The documentation about the usage of the application is available here.
License
This project is released under MIT license.
Contributing
If you have any question about the usage of the application, do not hesitate to open a discussion
If you want to report a bug or provide a feature, do not hesitate to open an issue or submit a pull request
📈 近 7 天 Star 趋势
🏆 排名变化趋势
📋 历史上榜记录
| 日期 | 榜单 | 排名 | 周期新增 | 总 STAR |
|---|