📄 仓库 README
在 GitHub 查看 ↗Ars0n Framework v2
About • Download & Install • Updating • Getting Started • Workflows • MCP Server • Troubleshooting • FAQs • YouTube • LinkedIn
🚨 Beta 0.1.2 Out Now!! 🚨
If you haven't been keeping up with my progress on the tool, I just released a massive update that includes an MCP server that allows an AI Agent (or collection of agents) to do anything a user can through the UI. I want to be super clear, though: THIS TOOL IS NOT DESIGNED TO REPLACE MANUAL BUG BOUNTY HUNTING WITH AI! Instead, my framework is designed to allow a human researcher to work seamlessly with both an AI system and a wide range of open-source tools, leveraging each for their specific advantages.
I've spent a lot of time meeting/chatting with successful bug hunters over the last six months now that AI has become a central part of everyone's workflow. The consistent thread I saw was that the most successful hunters had a deep understanding of the strengths and weaknesses of AI, automated tools, and humans. Using this deep understanding, those successful researchers broke down their bug hunting methodology into thousands of individual steps and, based on what was needed, identified whether it's best solved by a human, AI, or automted tool.
~ Human creativity will always be the key to success. Humans have the unique ability to come up with ideas that have never been thought of before. This is the "secret sauce", AI hunting hasn't changed that. If you're doing the same thing everyone else is doing, you'll find the same bugs everyone else is finding.
~ AI, specifically LLMs, excel in two areas: Converting unstructured data to structured data and building dynamic automated workflows that include complex decision-making. The framework's MCP server includes 150+ tools to facilitate that process, as well as an "Education Layer" that provides your AI system with the knowledge of an experienced hunter.
~ And finally, when you have a repetitive task that needs to be done fast, we pass those over to one of 50+ battle tested open-source scanning tools.
This combination is what successful bug bounty hunters are doing today. My goal is to make a clear path for beginners to start hunting in the same way, as soon as possible!
My full bug bounty hunting methodology built into a single framework! Automate the most common bug bounty hunting workflows and Earn While You Learn!
The goal of this tool is to eliminate the barrier of entry for bug bounty hunting. My hope is that someone can pick up this tool and start hunting on day one of their AppSec journey 🚀
🤠 Did you know that over 95% of scientists believe there is a direct correlation between the amount of coffee I drink and how quickly I can build new features? Crazy, right?! Well, now you can test their hypothesis and Buy Me a Coffee through this fancy button!! 🤯
About
Howdy! My name is Harrison Richardson, or rs0n (arson) when I want to feel cooler than I really am. The code in this repository started as a small collection of scripts to help automate many of the common Bug Bounty hunting processes I found myself repeating. Over time, I built these scripts into an open-source framework that helped thousands of people around the world begin their bug bounty hunting journey.
However, the first implementation of the framework had a wide range of issues. The majority of the problems were a result of the tool never being designed with the intent of being shared as an open-source project. So I got to work on a version 2 that would solve these problems and bring my vision to life!
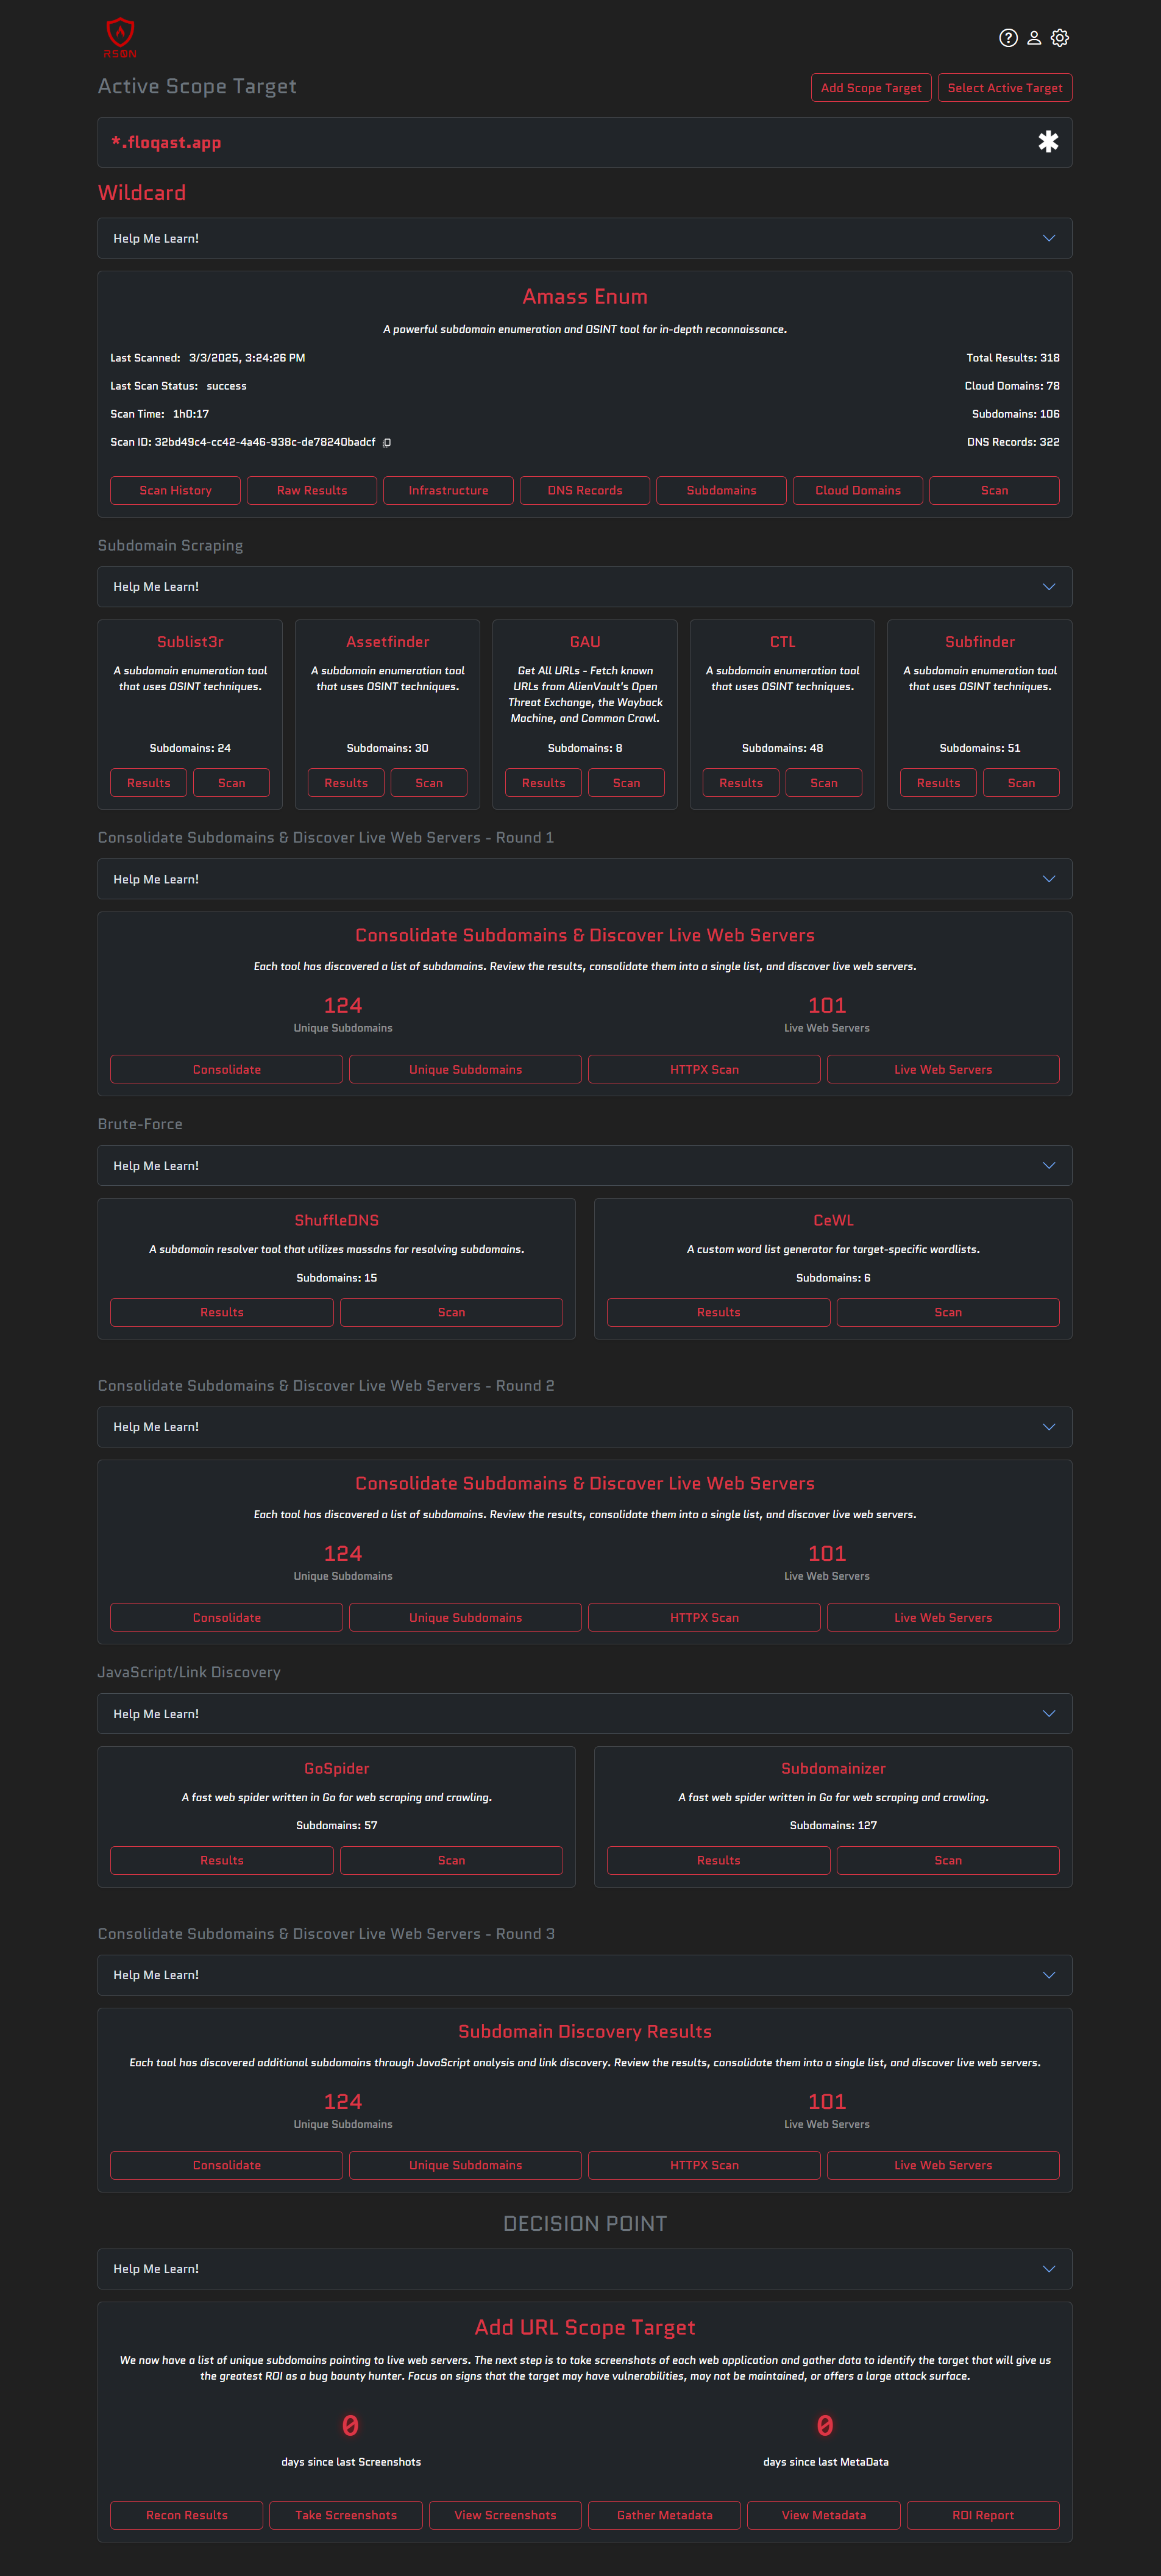
The Ars0n Framework V2 is designed to be a tool that allows people to start REAL bug bounty hunting against actual targets on day one! The framework acts as a wrapper around 50+ widely used bug bounty hunting tools and a clever UI design forces the user into a correct hunting methodology. It is literally impossible to use this tool without going through rs0n's process!
The results of each tool are stored in a central database and can be used for understanding/visualizing the target company's attack surface. Each section also includes a "Help Me Learn!" dropdown that includes a lession plan to help the user understand what part of the methodology they are at, what they are trying to acheive, and most importantly the "Why?" behind it.
My hope is that this modular framework will act as a canvas to help share what I've learned over my career to the next generation of Security Engineers! Trust me, we need all the help we can get!!
Pre-Alpha Demo Videos
The Ars0n Framework v2 Includes All These Tools And More!
Amass - Advanced attack surface mapping and asset discovery tool for security research
Subfinder - Fast and reliable subdomain enumeration tool with multiple data sources
Sublist3r - Fast subdomain enumeration tool using various search engines and data sources
Assetfinder - Find assets related to a domain using various data sources and APIs
Httpx - Fast and multi-purpose HTTP toolkit for web reconnaissance and scanning
GoSpider - Fast web spider written in Go for crawling and extracting URLs
Subdomainizer - Advanced subdomain enumeration tool with multiple discovery methods
CeWL - Custom word list generator that spiders websites to create targeted wordlists
ShuffleDNS - Mass DNS resolver with wildcard filtering and validation capabilities
Nuclei - Fast and customizable vulnerability scanner with extensive template library
Katana - Fast and powerful web crawler for discovering hidden endpoints and content
FFuf - Fast web fuzzer with support for multiple protocols and advanced filtering
GAU - Get All URLs tool that fetches known URLs from various historical data sources
CTL - Certificate Transparency Log tool for discovering subdomains from SSL certificates
DNSx - Fast and multi-purpose DNS toolkit for running multiple DNS queries
Cloud Enum - Multi-cloud OSINT tool for enumerating public resources in AWS, Azure, and Google Cloud
Metabigor - OSINT tool for network intelligence gathering including ASN and IP range discovery
GitHub Recon - GitHub reconnaissance tool for discovering organization mentions and domain patterns
Naabu - Fast port scanner for discovering open ports and services
Reverse Whois - Reverse WHOIS lookup using Whoxy to find domains registered by the same entity
SecurityTrails - Comprehensive DNS, domain, and IP data provider for digital asset discovery
Censys - Internet-wide scanning platform for discovering and monitoring assets
Shodan - Search engine for internet-connected devices and services
waybackurls - Fetches historical URLs for a host from the Wayback Machine
LinkFinder - Extracts endpoints and paths out of JavaScript files
📈 近 7 天 Star 趋势
🏆 排名变化趋势
📋 历史上榜记录
| 日期 | 榜单 | 排名 | 周期新增 | 总 STAR |
|---|